Every finding, in full resolution.
Audit in high definition.
AuditHD runs internal audits, quality reviews and compliance assessments for banks, lenders, listed companies and large enterprises. Ready-made country packs load each regulator's rules for Pakistan, Saudi Arabia, the UAE, Bahrain, Qatar, Kuwait, Oman, the EU and the US. Every finding is traced to its criteria, its evidence and the person who signed it off, AI drafts review comments that cite the clause, and every step is recorded in a tamper-evident trail.
Register with your work email, choose a country pack, and a fictional bank opens in your browser. Run AuditHD as SaaS or in your own data centre.
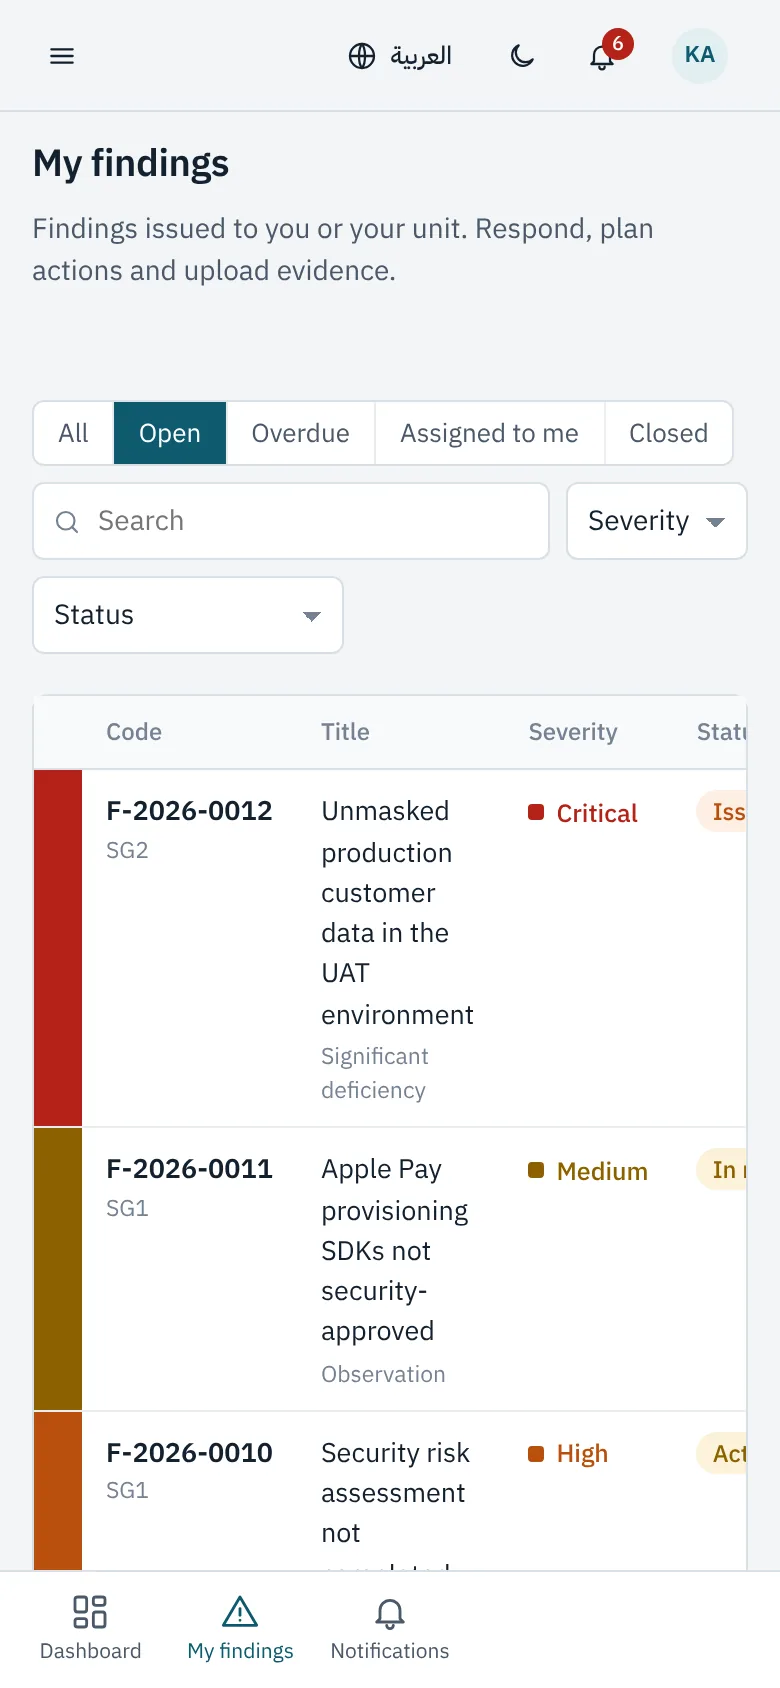
Unmasked production customer data in the UAT environment
- Condition
- 18,400 production customer records were copied to UAT on 2 October. Seven vendor testers have access.
- Criteria
- ISO 27001 A.8.11 SAMA CSF 3.3.3 Saudi PDPL
- Cause
- The refresh script ran without its masking step, which was switched off during troubleshooting.
- Effect
- Personal data exposed to people without a business need: a possible PDPL breach.
- Action
- Purge the copy, restore masking, review access logs, assess PDPL notification.
4cf7…2f3fA ready-made pack for every country you report to.
Each country pack holds its regulators' frameworks, audit checklists, the calendar of regulatory deadlines, record-retention periods and rating rules, for banks, lenders, listed companies and large enterprises. License the countries you need. International standards are included with every licence.
103 frameworks and regulations, 55 ready-to-run checklists and 176 recurring regulatory deadlines across 10 packs. Explore the country packs
Know your risks before the auditor does.
Units test their own controls every quarter, and MARS™ turns what they find into a register management signs and hands to the external auditor or regulator.
Risk and control self-assessment
Each unit tests its own controls every quarter; another unit re-performs a sample, the second line challenges and signs off, and internal audit adds its own results. Residual risk is rated on the same scale across the organisation.
MARS™ management awareness rating
Every issue found internally is registered with its residual risk, action plan and due date, and acknowledged by the head of the unit. When an external review starts, the register is frozen and handed over; when the findings arrive, MARS™ rates how much management already knew.
Built for the people who sign off.
One platform for the teams that audit and certify financial institutions and large enterprises, in Pakistan, the GCC and beyond.
Internal audit and QA
For banks, financial institutions and large enterprises. Plan by risk, run stage-gate QC on every change request, and show the audit committee where the bank stands.
- Risk-based annual plan
- Stage-gate QC for IT changes
- Quarterly RCSA with peer review and second-line sign-off
- Auditee responses on any phone
- Committee dashboards in Arabic or English
External audit and assurance firms
Run every client engagement on one platform, keep each client's data apart, and deliver reports in both languages.
- Reusable work programmes
- Separate, isolated data per client
- Evidence integrity you can prove
- Bilingual Word reports
ISO and CMMI consultancies
Gap assessments, internal audits and maturity scoring against ISO 27001, ISO 9001 and CMMI V3.0.
- Clause-by-clause checklists
- Maturity and capability scoring
- Cross-mapped controls
- Corrective actions to closure
The whole audit cycle, in one place.
Each stage hands its work to the next, so nothing is retyped and nothing goes missing between spreadsheets.
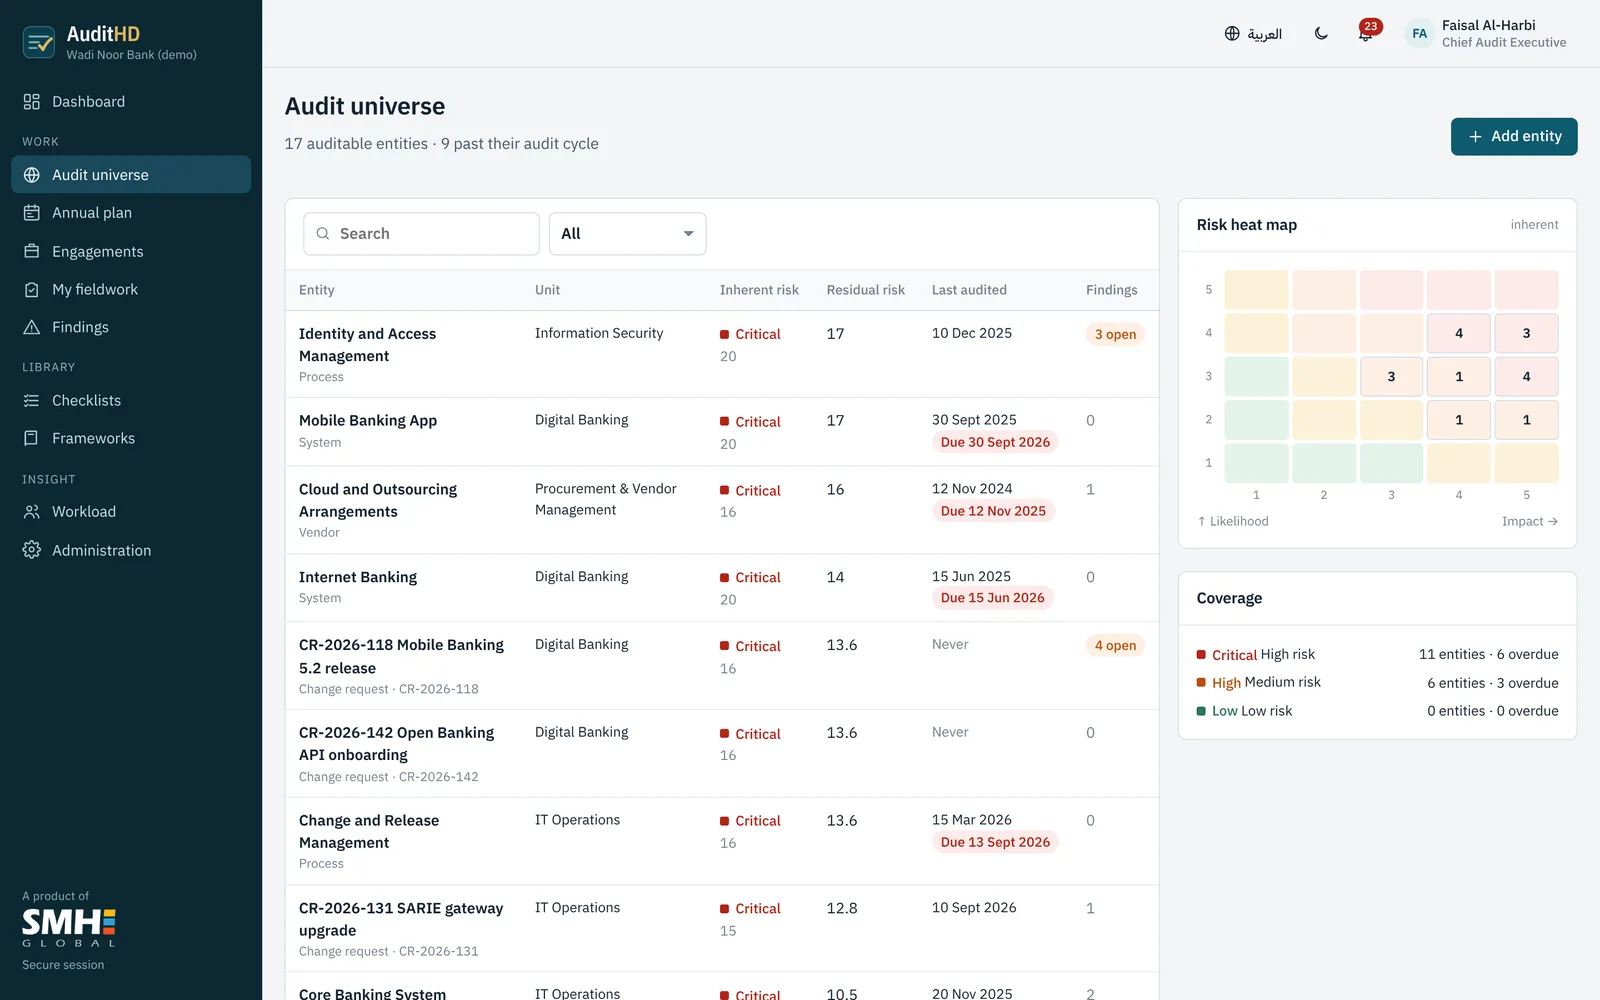
- Score every entity by likelihood, impact and control strength, and see the heat map update.
- Build the annual plan from the highest-risk areas, with quarters, owners and budgets in hours.
- Track plan completion and slippage on the committee dashboard.
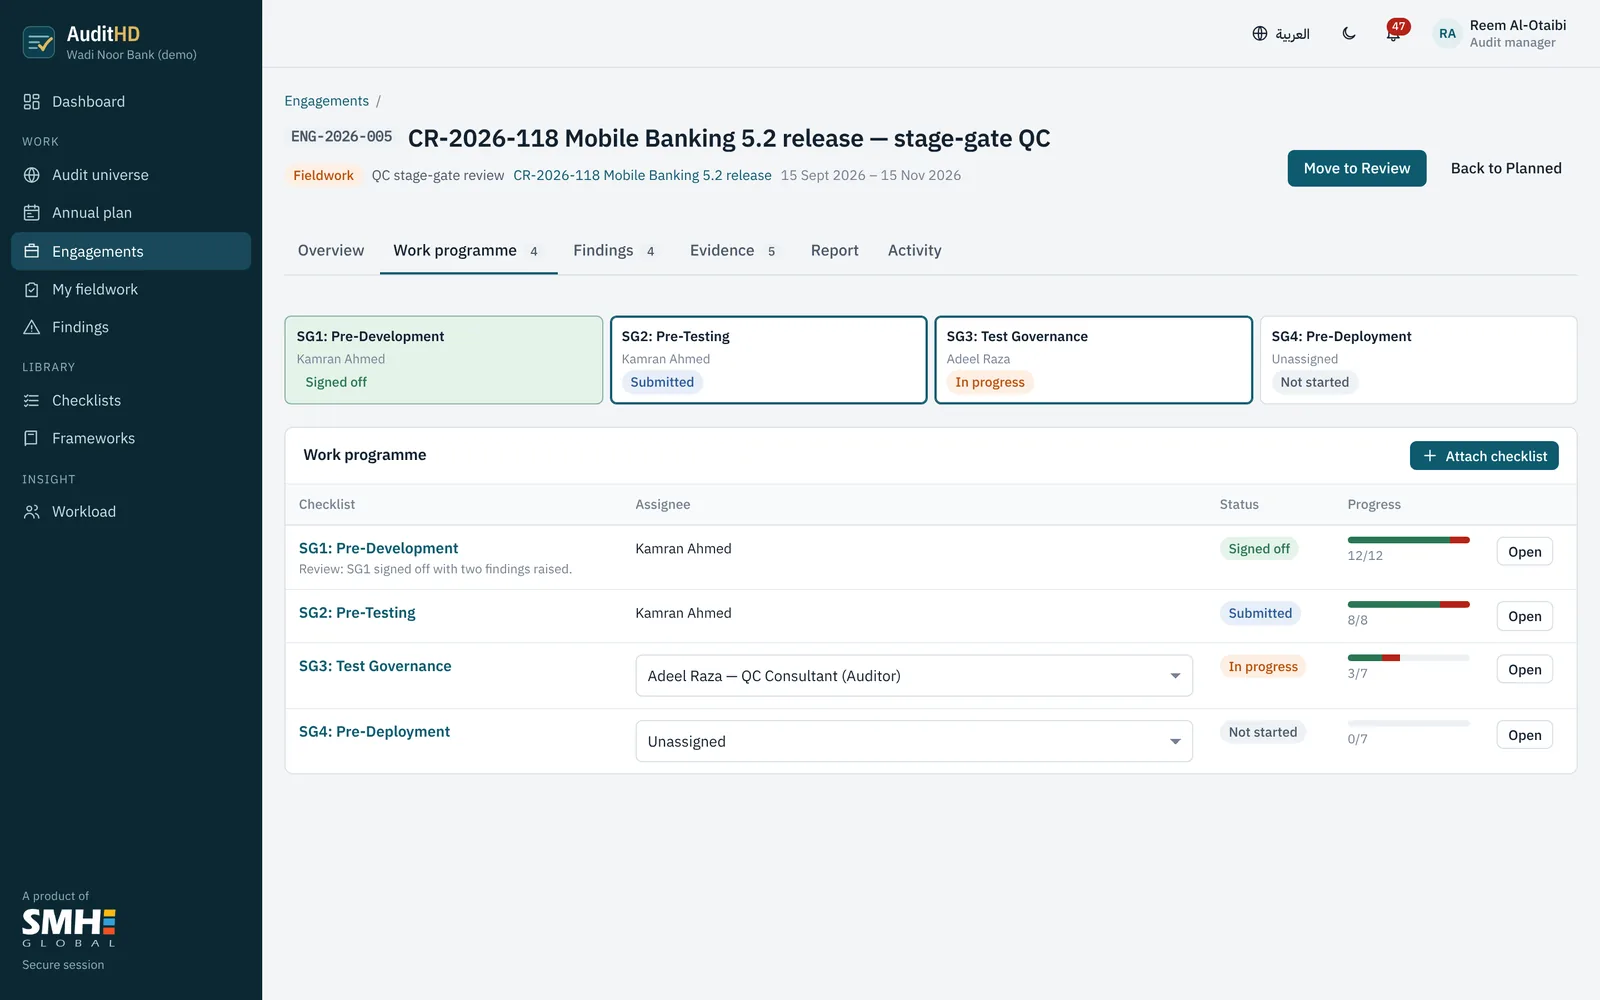
- Attach a framework checklist (SAMA CSF, NCA ECC, ISO 27001 and more) or build your own.
- Split a checklist by stage gate or section and assign each part to a different reviewer.
- See everyone's load before you assign, and rebalance in one click.
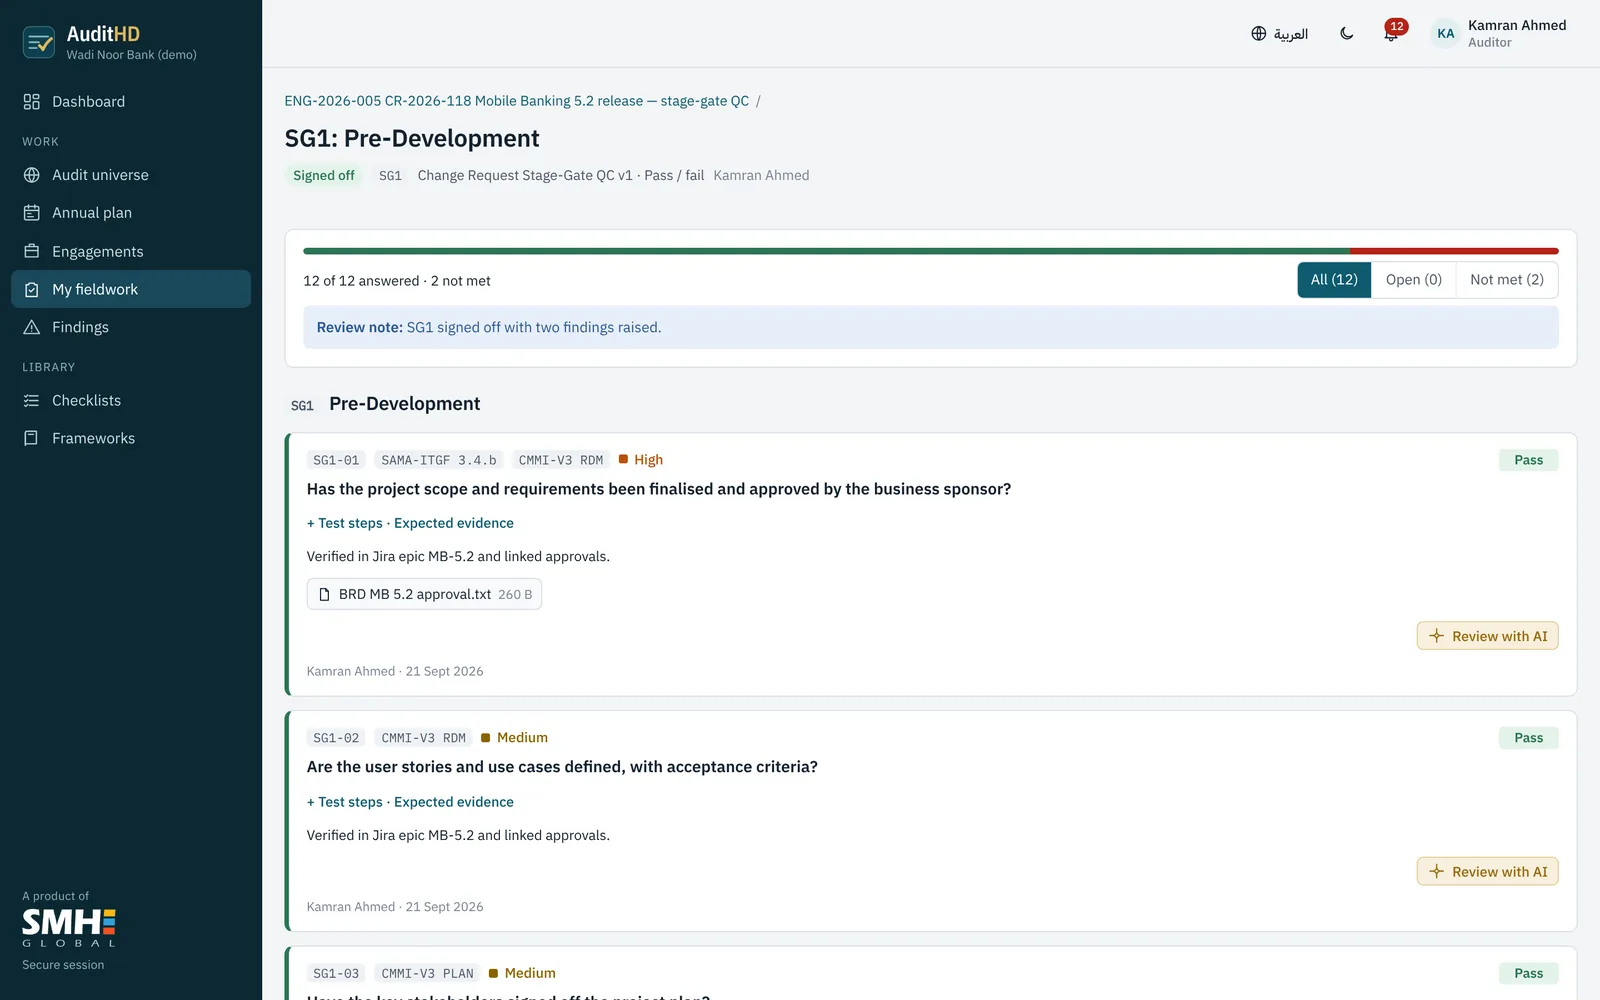
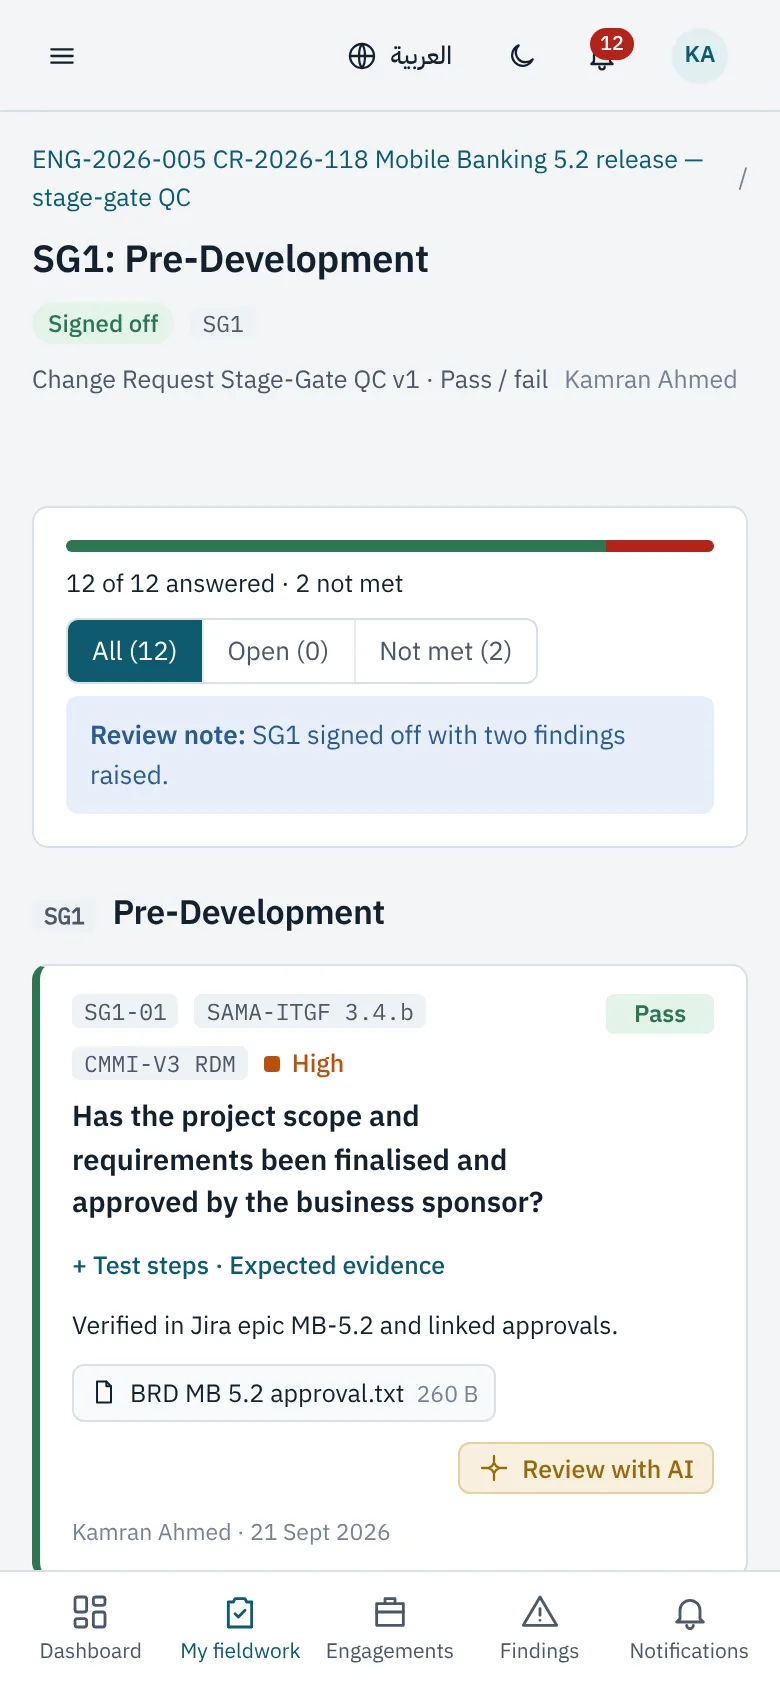
- Record pass, fail or maturity scores with notes and evidence on each item.
- Take photos on a phone with time and location; work offline and sync later.
- Ask the AI reviewer to check that the note, result and evidence agree before you submit.
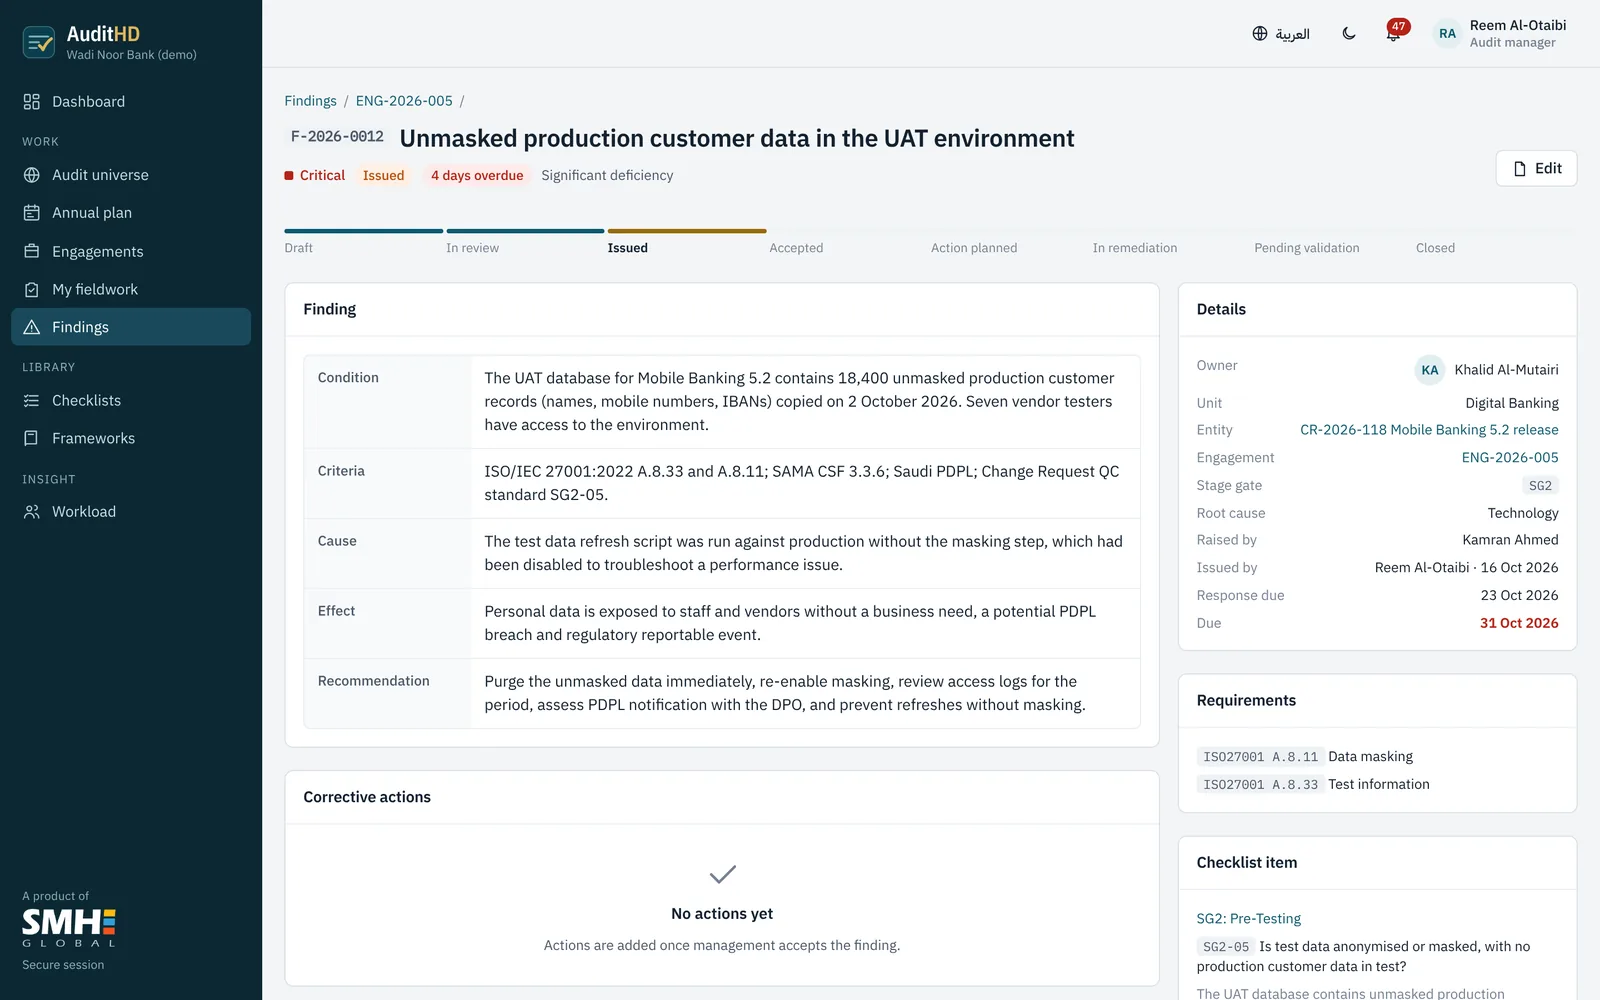
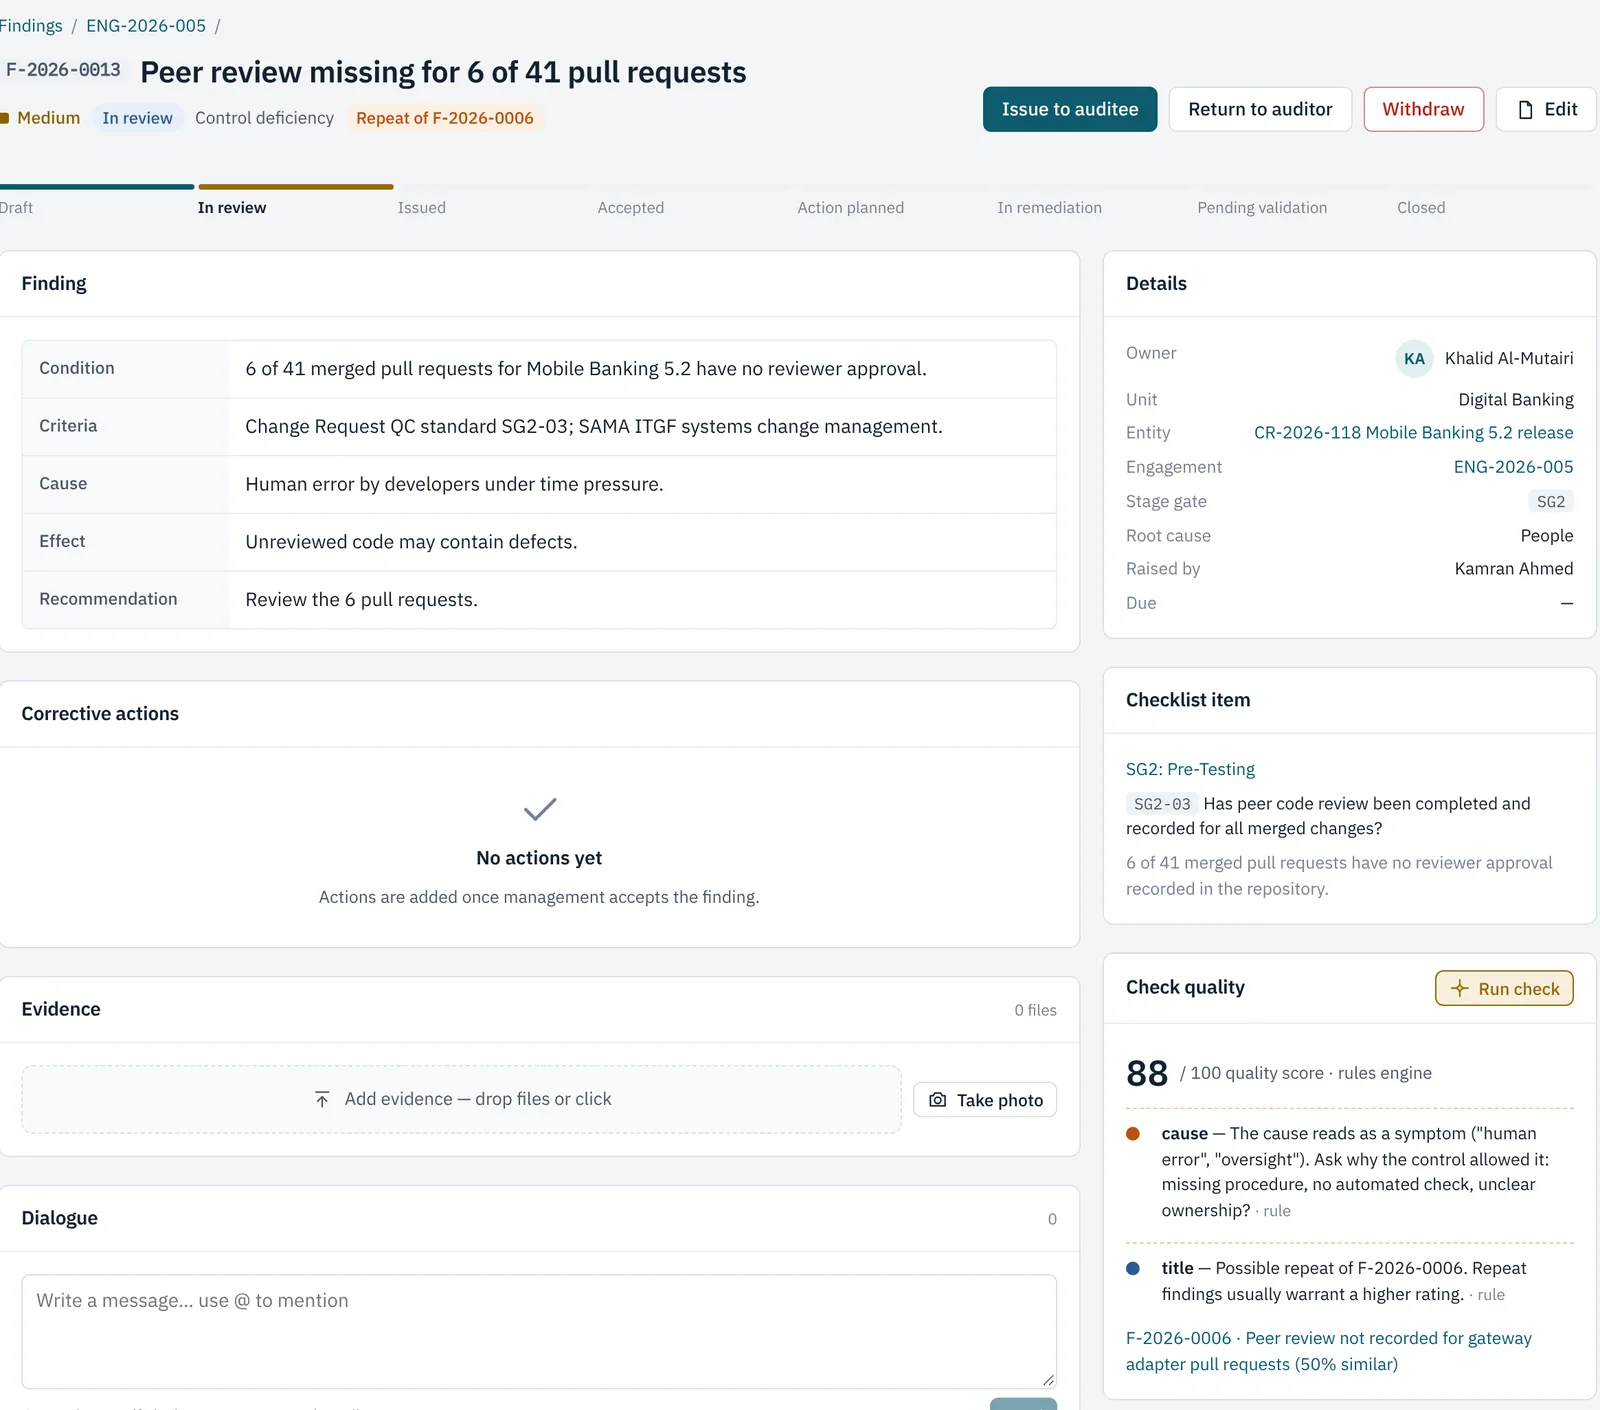
- Write findings as condition, criteria, cause, effect and recommendation, linked to the clause.
- The person who raised a finding cannot issue it; a reviewer must.
- An automatic quality check flags vague root causes and repeat findings.
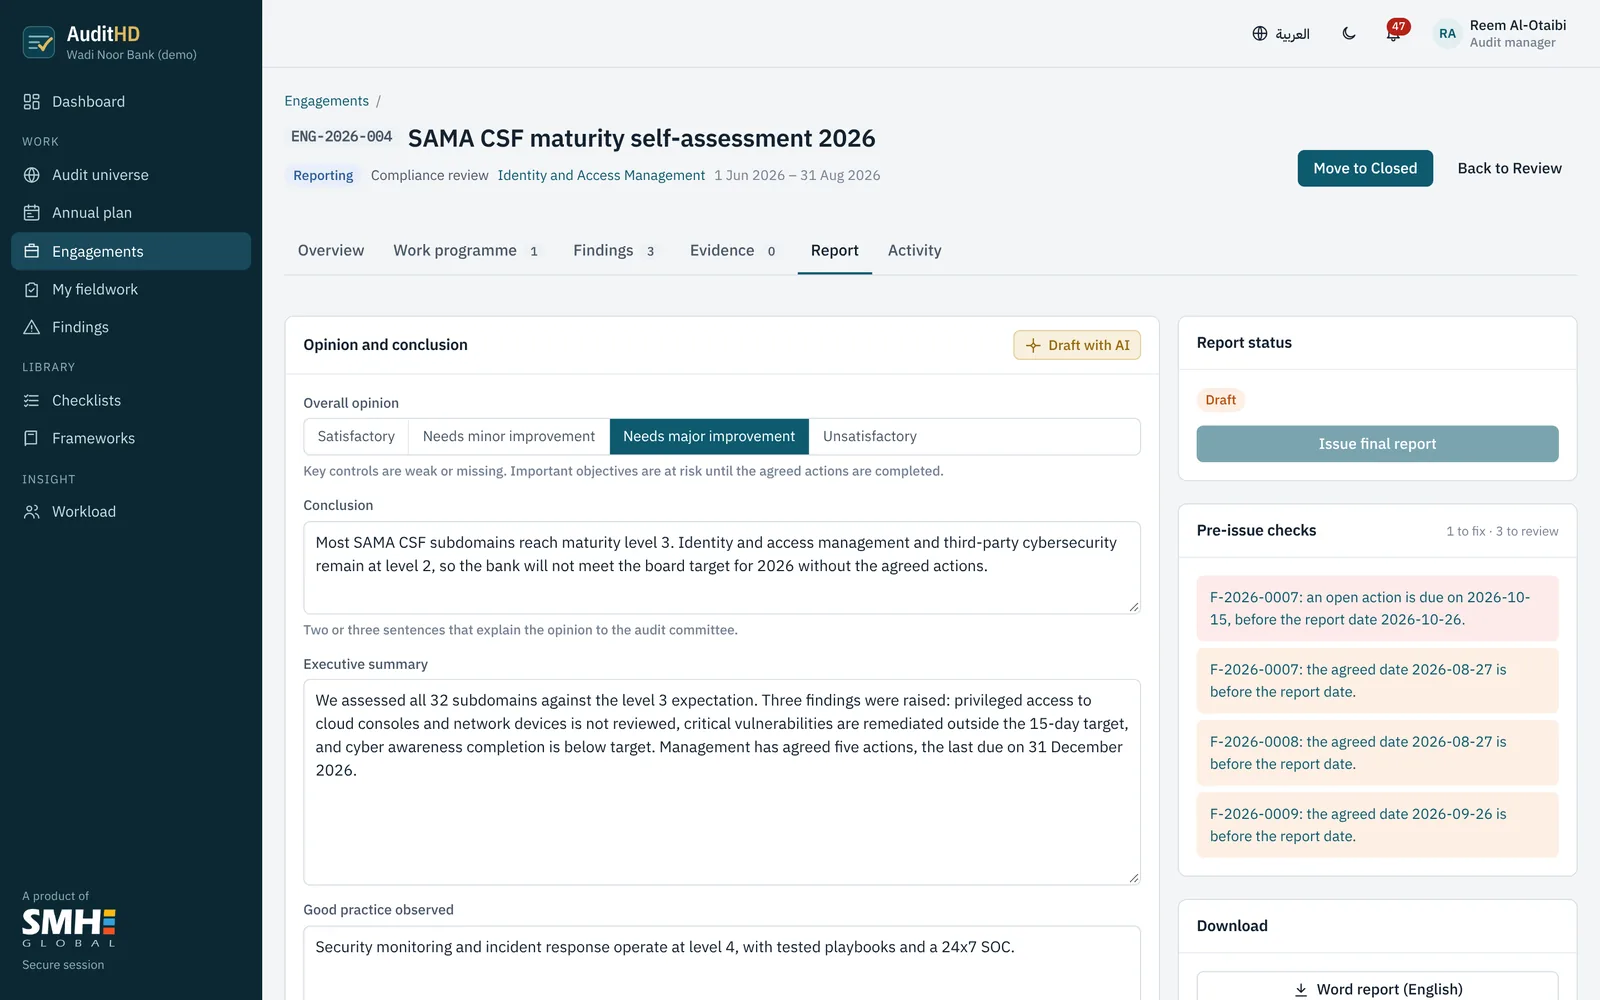
- Auditees accept or dispute, plan actions and upload proof from their phones.
- SLA reminders and escalations go out automatically; extensions need approval.
- Issue Word reports in English and Arabic and Excel registers in one click.
AI that cites the clause, and waits for an auditor.
AuditHD's AI reviewer reads the checklist item, the evidence and the requirement, then suggests what to fix. It never issues a finding, closes an action or changes a record on its own.
- Checks that each result, note and piece of evidence agree.
- Flags vague root causes like "human error", and spots repeat findings.
- Drafts findings, checklists and committee summaries for you to edit.
- Translates between English and Arabic.
You choose where the model runs.
Off
Built-in rules check every workpaper. Nothing leaves the server.
On-premises only
Open models on your own GPU server, through Ollama or vLLM.
In-country cloud
A provider hosted in your country, for data-residency rules.
Any approved
Claude, OpenAI or Azure OpenAI, with personal data redacted first.
A record the regulator can trust.
Every change, from a checklist answer to a closed action, is written to an append-only log. Each entry carries the fingerprint of the one before it, so any edit or deletion shows up.
- Evidence files are fingerprinted (SHA-256) on upload and checked on every download.
- Verify the whole trail from the administration screen in one click.
- Each organisation's data is separated inside the database itself.
- Roles and maker-checker rules decide who can raise, issue and close.
- 383Finding issued by Reem Al-Otaibi, QC lead9b1e…77a0
- 384Comment added by Khalid Al-Mutairi, auditeec40d…1e9b
- 385Action plan accepted by Reem Al-Otaibi4cf7…2f3f
Works where the audit happens.
Branch visits, data-centre walkthroughs and site inspections rarely have good signal. AuditHD keeps working.
- Install it on any phone or tablet from the browser. No app store needed.
- Answers saved offline sync automatically when you are back online.
- Photos are taken in the app, with time and location attached.
- Auditees accept findings and upload proof from their phones.
- Full Arabic interface, right to left, and reports in both languages.
Runs where your data has to stay.
Banks in Saudi Arabia, the UAE and Pakistan often need audit data kept in-country or on their own servers. AuditHD is built for that.
| SaaS | On-premises | Air-gapped | |
|---|---|---|---|
| Who runs it | SMH Global Services | Your IT team, with our support | Your IT team, installed from an offline package |
| Where data lives | A cloud region agreed with you | Your data centre | Your isolated network |
| AI options | Any approved provider | Your choice, including on-premises models | Rules engine or on-premises models |
| Updates | Automatic | One command, with a backup first | From an image archive you transfer in |
| Typical buyer | Audit and consulting firms | Banks and regulated companies | Banks with strict separation rules |
See it with your own checklists.
Open the live demo now, or book a walkthrough and we will load one of your frameworks or work programmes.